CrowdStrike Expands Continuous Identity Security to Address Autonomous AI Agents
At Fal.Con 2026, the cybersecurity giant outlined how its platform continuously authorizes non-human entities as automated activity outpaces human logins.
Traditional identity security models that grant implicit session trust upon initial authentication are facing pressure as autonomous software agents execute rapid sequences of API and tool calls. To prevent security breaches caused by non-human systems, cybersecurity vendors are transitioning toward continuous authorization architectures that validate individual operational requests in real time.
At its Fal.Con 2026 conference in Las Vegas, CrowdStrike Holdings Inc. highlighted new capabilities designed to extend continuous identity verification across autonomous AI workflows. CrowdStrike President Michael Sentonas detailed during his keynote presentation how the company's Falcon platform manages risk profiles for non-human identities operating within corporate networks.
The underlying capability relies on technology acquired through CrowdStrike’s $740 million purchase of SGNL, a deal announced in January that was launched commercially in June as Continuous Identity for AI Agents. The system inspects agent ownership, the calling entity, and the target device's security posture before granting approval for each action, applying identical evaluation standards to both human and non-human users.
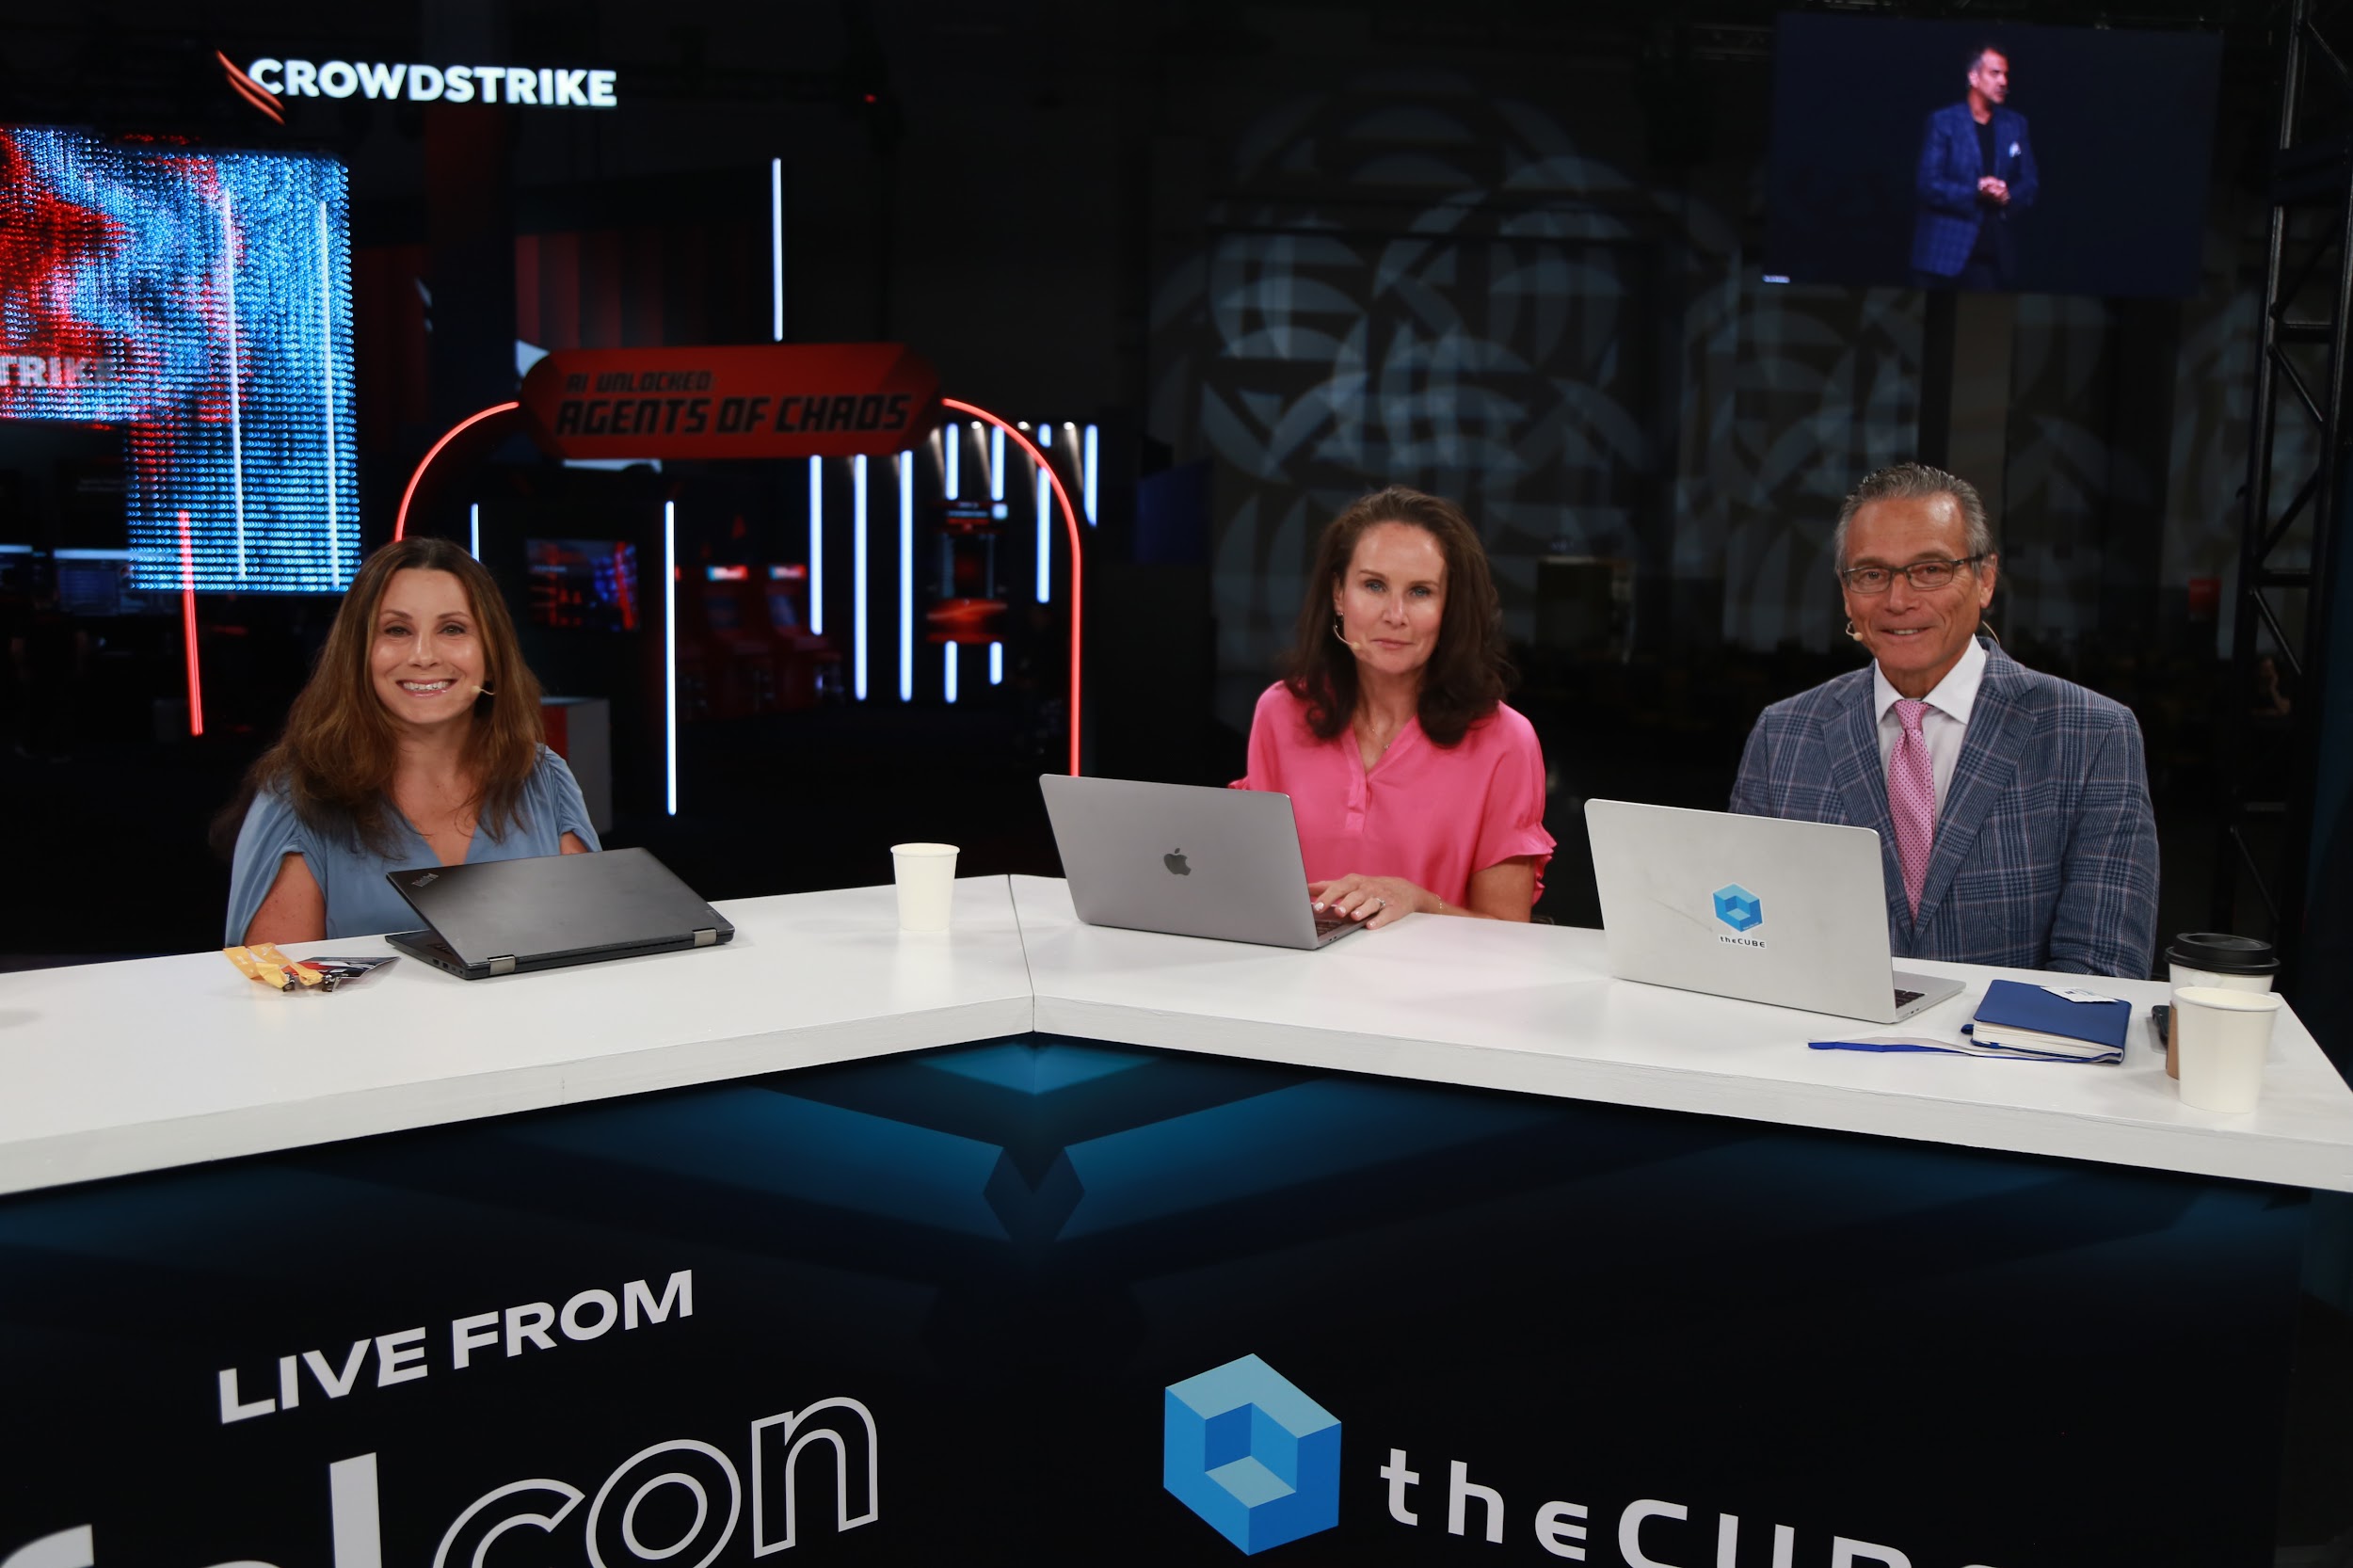
The platform updates were analyzed during a broadcast on theCUBE, SiliconANGLE Media’s livestreaming studio, where industry analysts discussed the operational demands facing automated security operations centers. Krista Case, principal analyst and practice lead for cyber resilience and security at theCUBE Research, observed that modern security controls must restrict autonomous tasks through brief, scoped permissions.
“It’s looking at continuous authorization, having that continuous approach, as AI agents are continuously accessing data and taking actions,” Case noted during the broadcast. She added that CrowdStrike’s technical model limits access permissions to specific tasks using short-lived authorizations that expire as soon as an operation finishes.
Maintaining visibility over autonomous software requires enterprise teams to monitor operational changes alongside standing permission lists. “It’s not just about understanding their privileges and what they should have access to,” Case said, adding that security teams must evaluate “how their behavior evolves over time and having the right safeguards in place to prevent them from going off the rails, whether maliciously or just through drift.”
The shift toward automated defense is being driven by the sheer volume of non-human network traffic. CrowdStrike researcher Adam Meyers told conference attendees that AI agents currently generate approximately 250 times more security detections than human employees do.
At the same time, recent threat intelligence from CrowdStrike shows that average electronic crime breakout times have dropped to 29 minutes, with the fastest recorded intrusion taking 27 seconds. Managing attacks at that scale requires both rapid response times and accurate risk validation. “It’s not just about the speed of detection and response,” Case stated. “It’s also the confidence: This is a true risk, we’re prioritizing it, and this is the right way to keep critical business services online.”
Sources
Written by
The Company Wire
Inside the companies building what’s next. Reporting on startups, technology, funding and the people shaping them.