Obscura Launches Two-Party VPN Architecture Designed to Prevent Traffic Logging
The service pairs QUIC obfuscation with independent Mullvad exit relays to separate user identities from web activity.
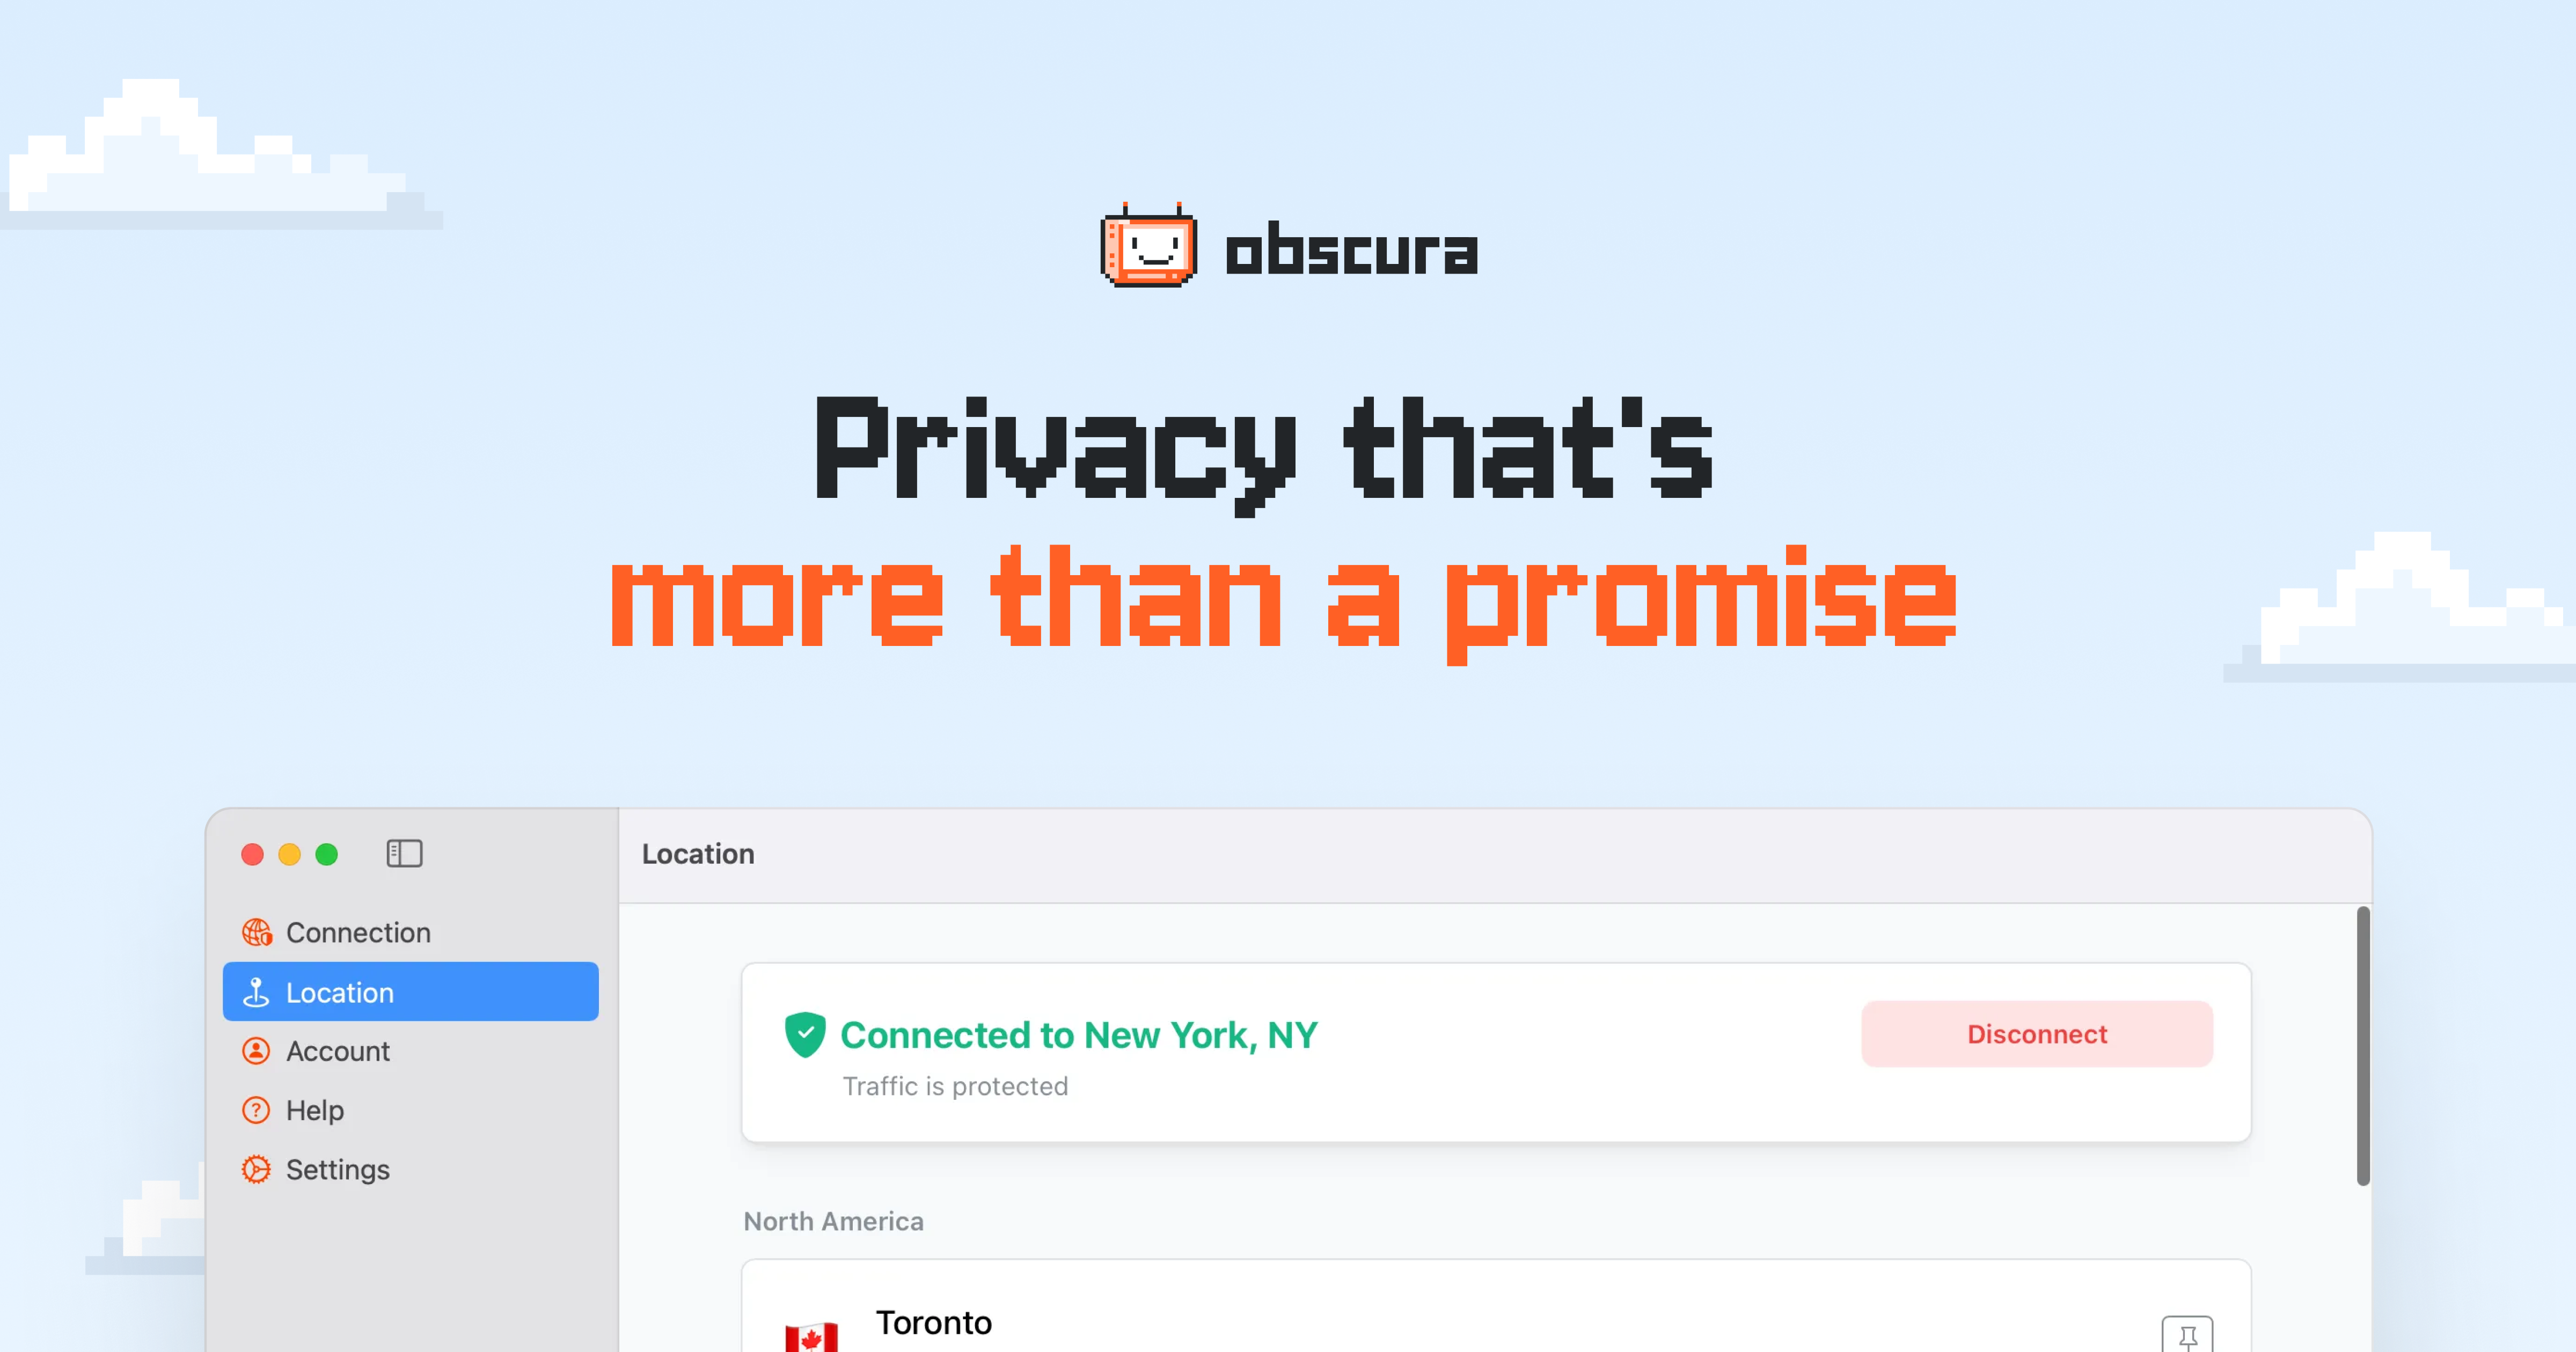
Obscura, a newly introduced virtual private network service, has launched an infrastructure model designed to prevent the service provider from monitoring or recording user internet activity, according to technical documentation shared on Hacker News (https://obscura.com/#faq-technical). The platform separates user identity from outgoing traffic by splitting routing across independent operational layers.
Commercial VPN providers frequently advertise "no-logs" commitments, which require subscribers to trust operational policies while the provider maintains visibility into both inbound user IP addresses and outbound network traffic. Obscura addresses this configuration through a two-party relay structure: Obscura operates the ingress relay, while exit servers are operated independently by VPN provider Mullvad.
Connections between user devices and Obscura's entry servers run over QUIC, the transport protocol underpinning HTTP/3, allowing VPN traffic to blend with standard internet traffic to resist network filters. Inside the QUIC wrapper, traffic is encrypted end-to-end via the WireGuard protocol directly to Mullvad's exit servers. Under this arrangement, Obscura receives the user's connecting IP address but cannot decrypt payload packets, while Mullvad processes destination traffic without visibility into the originating user identity. Obscura states that it does not log connecting IP addresses.
To limit data collection during signup, Obscura issues randomized account numbers rather than collecting names, email addresses, or phone numbers. The service supports payments through Bitcoin's Lightning Network and Monero, as well as credit card transactions processed through Stripe. Obscura notes that while Stripe may request an email address during card processing, Obscura does not store email information. Accounts support up to five simultaneous connections.
For verification, Obscura has published its client application source code on GitHub and stated plans to introduce reproducible builds. The application interface displays the active exit hop's WireGuard public key, enabling users to verify it against Mullvad's published keys. On macOS, the client runs as a sandboxed Network Extension without kernel-level system permissions.
Native client applications are available for macOS, iOS, Android, Linux (x64), and Windows (x64 and ARM64). Obscura also provides a WireGuard compatibility mode that generates standard configuration files for unsupported platforms, retaining the two-party relay architecture without QUIC-based traffic masking.
The engineering team behind the project includes contributors with background on the Nix RFC Steering Committee, the Go standard library random number generator, Monero bug bounty programs, hardware security token vulnerability fixes, and Bitcoin reproducible build initiatives. Obscura positions the two-hop architecture as a higher-throughput alternative to multi-hop onion routing networks like Tor for everyday internet usage.
Sources
Written by
The Company Wire
Inside the companies building what’s next. Reporting on startups, technology, funding and the people shaping them.