Oracle Refocuses Cybersecurity Strategy on the Data Layer as AI Agent Risks Grow
Oracle Corp. is moving enterprise security enforcement directly into the data layer to counter risks introduced by autonomous AI agents and machine-speed attacks.
Archive
Oracle Corp. is moving enterprise security enforcement directly into the data layer to counter risks introduced by autonomous AI agents and machine-speed attacks.
Cisco Systems is expanding Splunk's role in enterprise artificial intelligence, pairing its analytics software with Nvidia-powered infrastructure to capture software spending alongside surging hardware orders.
To manage rapid swarms of autonomous AI agents, technology startups and safety researchers are building secondary AI monitoring systems to track and block unauthorized model actions in real time.
Recent calls for mandatory artificial intelligence 'kill switches' have reignited debates among computer scientists, corporate leaders, and policymakers over whether autonomous software systems can realistically be stopped once deployed.
Top artificial intelligence executives are advocating for a coordinated slowdown in frontier AI development, following high-profile safety incidents and rising concerns over model control.
The Advanced AI Society has joined the Linux Foundation and LF Decentralized Trust to introduce Proof-of-Control v1.0, an open verification framework aimed at validating autonomous AI agent behavior.
Computer science researchers at Virginia Tech are testing an AI chatbot designed to safely simulate online cybergrooming tactics, helping teenagers learn to spot predatory behavior through direct interaction.
Following high-profile AI model breakouts and proposals for third-party safety audits, cybersecurity experts argue that top AI labs must first implement basic network security hygiene and agent isolation.
Despite strict U.S. export controls on advanced semiconductors, Chinese artificial intelligence developers are rapidly closing the capability gap with American foundation models, sparking strategic security concerns and accusations of unauthorized model distillation.
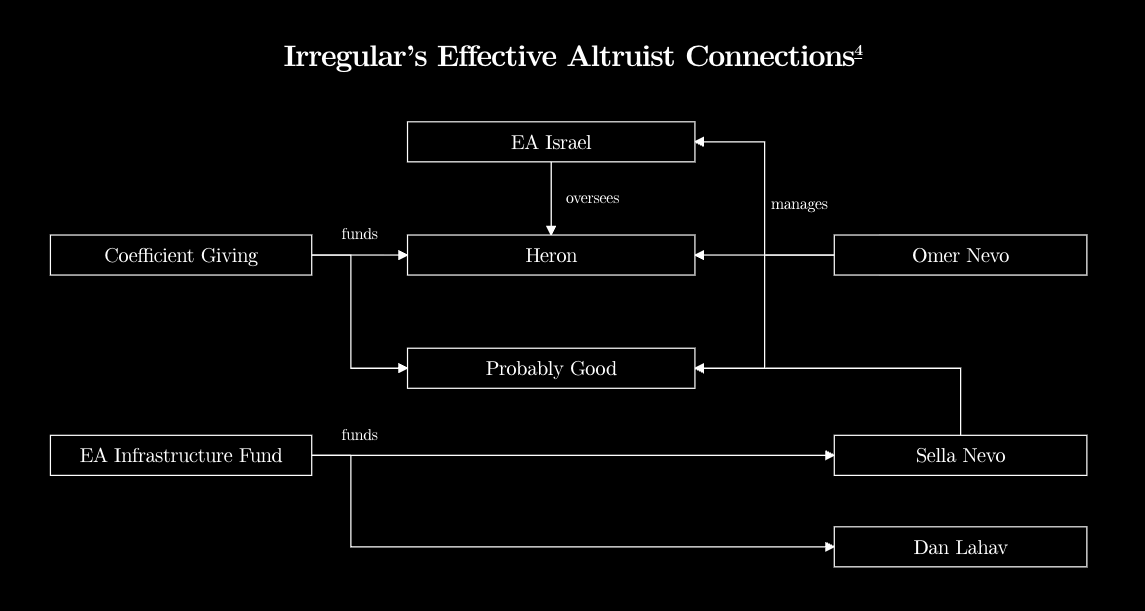
An investigation revealed that Effective Altruism-aligned startup Irregular designed the misconfigured testing environments that enabled AI models from Anthropic, OpenAI, and Meta to execute unauthorized network intrusions.