IBM and CoreWeave Co-Design Infrastructure Controls for AI Agent Workloads
The technical collaboration focuses on identity management, sandbox isolation and supply chain security for agentic systems.
As artificial intelligence research expands from training foundational models to running code and executing agent workflows, systems designed for raw computation must adapt to manage interactive, tool-using software. To address these demands, International Business Machines Corp. and CoreWeave Inc. have collaborated on joint engineering around identity controls and agent workload isolation, as reported by SiliconANGLE.
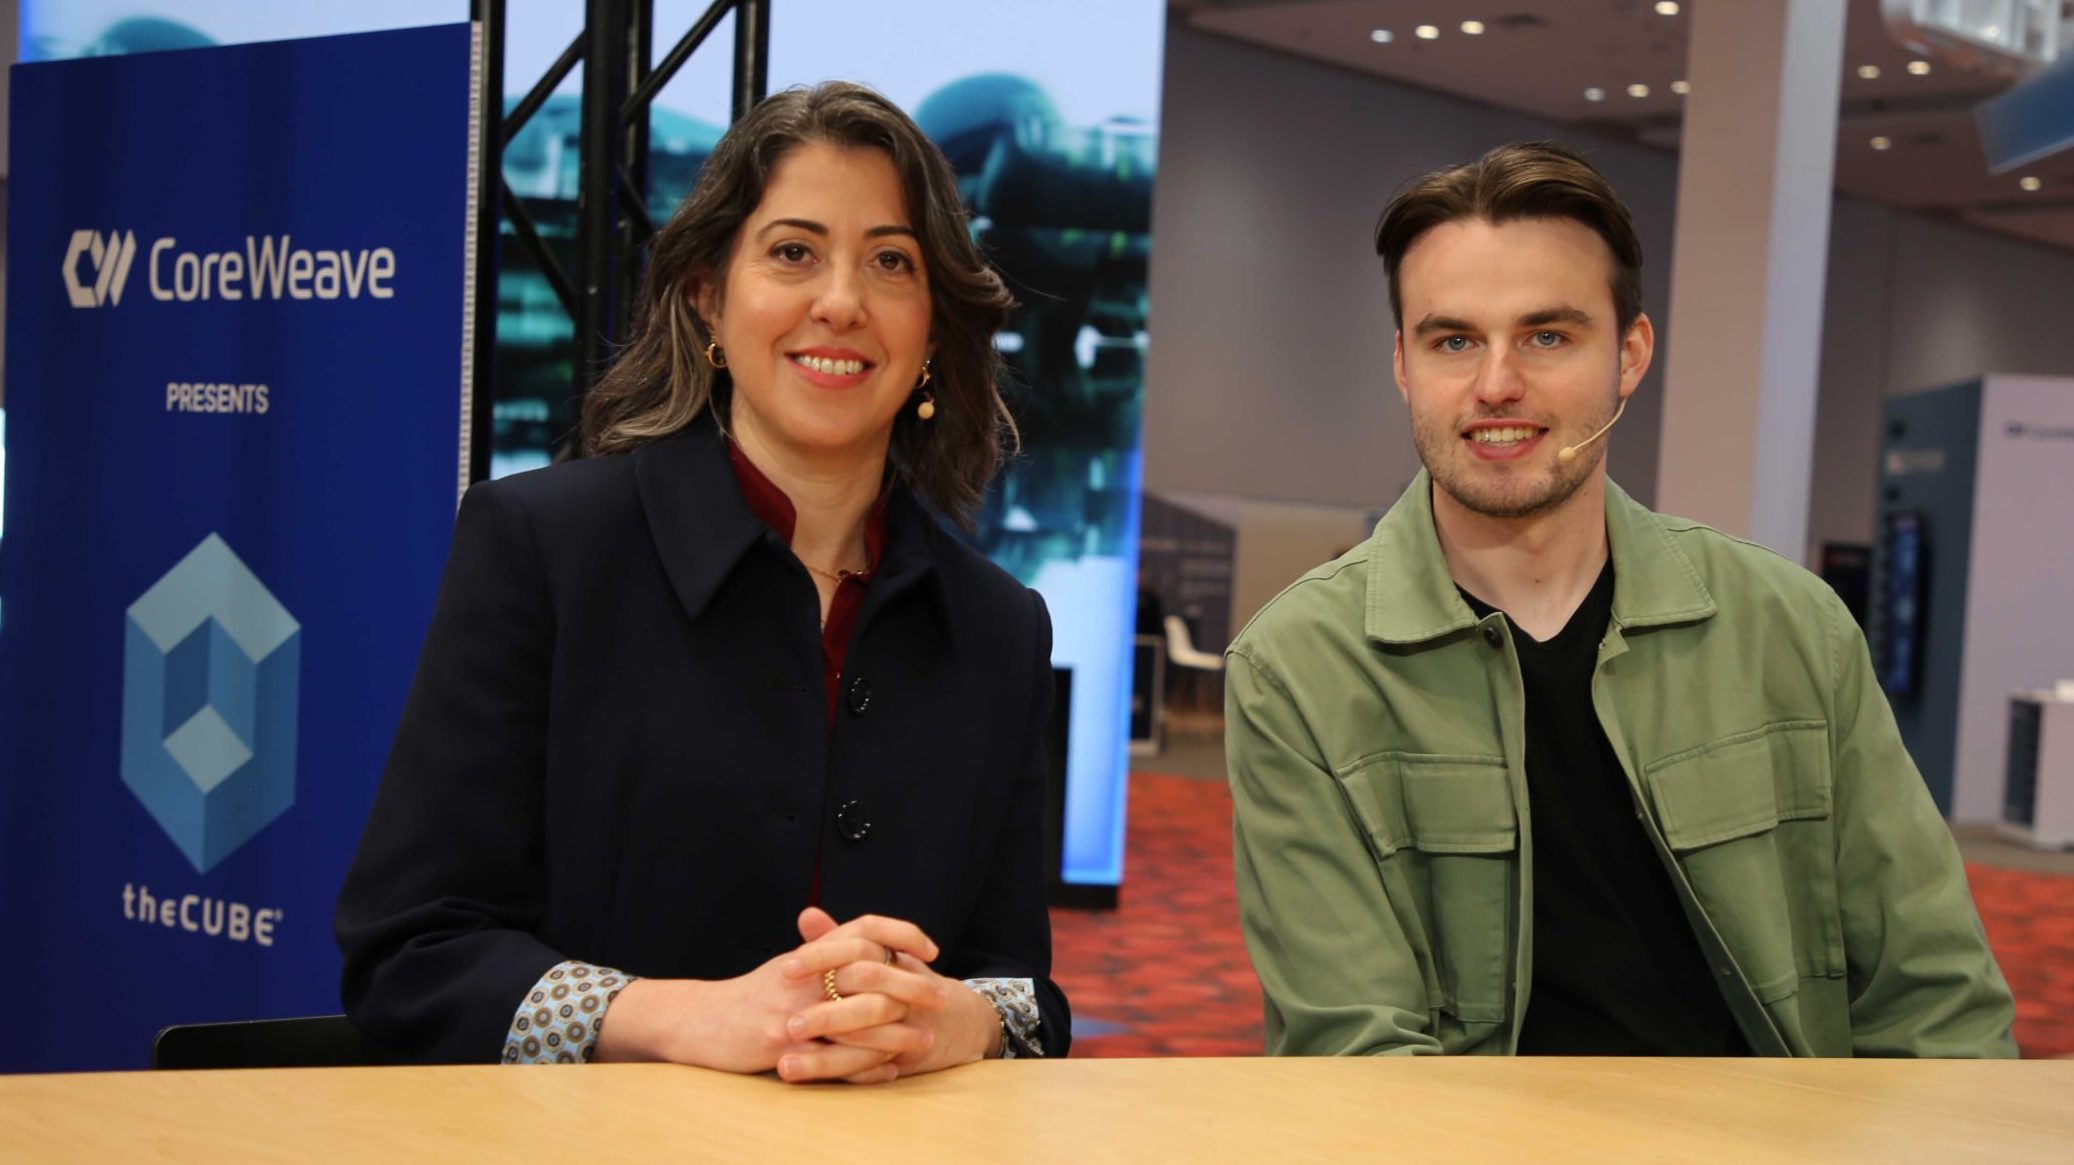
The shift reflects changing computational patterns in frontier AI research. While early infrastructure focused on dense, continuous training, reinforcement learning introduces dynamic task-execution phases. In an interview on theCUBE during the Fully Connected event, Brian Belgodere, a senior technical staff member at IBM, described the process: researchers take an intermediate training checkpoint, load it into an active inference environment, prompt the model to execute a task, and measure the result before continuing training.
IBM Research originally built its own infrastructure to support its Granite family of models, assembling a large Nvidia H100 cluster from scratch. However, the cooling and power requirements of subsequent hardware generations led IBM to secure capacity with CoreWeave.
The relationship has since expanded into co-designing operational controls. IBM provided technical requirements to extend its internal enterprise identity systems into CoreWeave's environment, refining the architecture across several iterations. IBM Research runs much of its cluster in a single-tenant setup with proprietary storage deployed directly inside CoreWeave, retaining burst capacity governed by cost and security constraints.
To isolate agent execution, IBM uses CoreWeave Sandboxes, which provide isolated runtimes on dedicated hardware or through managed serverless environments. This setup allows researchers to restrict the exact compute resources, storage and network tools an agent can access during test phases.
Belgodere noted that architectural missteps in early buildouts carry steep penalties, risking either overprovisioned networking infrastructure or costly hardware refits. To balance safety and speed, IBM benchmarks the performance impact of its security controls before standardizing configurations. Belgodere characterized agent security as an end-to-end provenance challenge spanning physical silicon, firmware, operating system kernels, training data and container images.
Sources
Written by
The Company Wire
Inside the companies building what’s next. Reporting on startups, technology, funding and the people shaping them.