Nvidia Introduces 'Scale-In' Architecture to Govern Enterprise AI Agents
The chipmaker pairs BlueField DPUs, DOCA software, and the open-source OpenShell runtime to run out-of-band monitoring and access controls across AI factories.
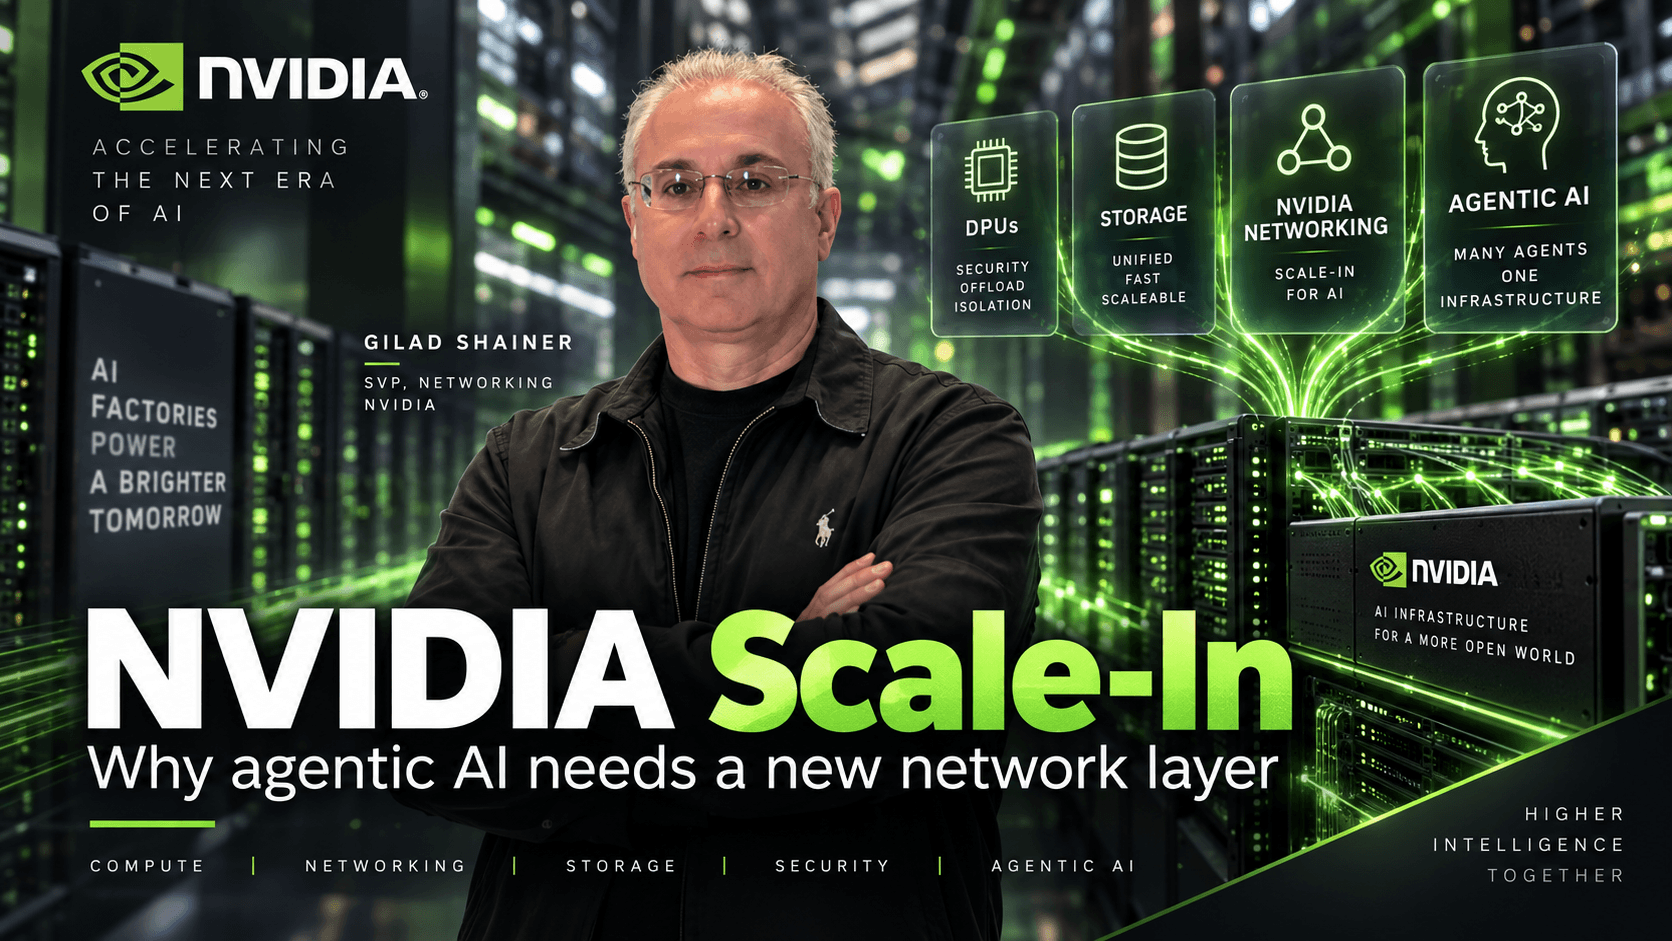
Nvidia Corp. is expanding its data center networking architecture to address operational security and access control for autonomous artificial intelligence agents. The company is introducing an infrastructure category it calls "scale-in," which broadens the role of its data processing units from traditional workload offload to cross-facility governance across AI factories. The strategy was detailed by Gilad Shainer, Nvidia senior vice president of networking, in an interview reported by SiliconANGLE .
Scale-in complements Nvidia's existing scale-up, scale-out, and scale-across architectures. Whereas early generative models primarily handled discrete query-and-response interactions, agentic AI systems execute iterative operational flows involving repeated model queries, enterprise data retrieval, application tool calls, and automated task execution. According to Shainer, governing these multi-step workflows requires moving beyond north-south boundary security at the network perimeter to monitor east-west internal traffic moving across compute, memory, and storage subsystems inside the data center.
The scale-in design isolates governance and security enforcement from the application domain where agents run. Nvidia's framework pairs its BlueField data processing unit hardware with DOCA software and its newly introduced OpenShell agent runtime. OpenShell version 0.1.0 provides an open-source execution layer that defines and enforces system permissions through sandboxing, controlled service access, credential management, and formal policy analysis. The runtime supports agentic frameworks including Codex, Claude Code, Pi, and Hermes across enterprise workloads, frontier research, and physical AI systems.
At the hardware layer, the BlueField-4 DPU integrates a CX-9 SuperNIC with an onboard Grace central processing unit, expanding secure traffic coverage to 7.2 terabits compared with 400 gigabits in previous access-path configurations. By utilizing embedded silicon security engines and collecting telemetry across compute, memory, and storage, the DPU operates in a dedicated administrative domain separate from the primary GPUs and CPUs, such as Vera, running the underlying models. This out-of-band architecture is structured to eliminate performance penalties on active application workloads while managing cryptographic keys, encryption, and ConnectX interfaces.
Shainer compared the architectural separation to historical software isolation models like virtualization, web browsers, and hypervisors, which enabled enterprise deployment of untrusted software by enforcing external constraints. The approach draws functional parallels to the domain isolation seen in cloud infrastructure platforms such as AWS Nitro. By running governance tasks on the Grace CPU inside the DPU, infrastructure controls operate independently of the agent's application code.
Scale-in also addresses memory bottlenecks caused by growing context sizes during complex agent operations. When agent workloads exceed standard compute server memory capacity, Nvidia routes data through CMX and STX architectural elements, utilizing BlueField as a storage controller for context infrastructure alongside traditional GPU-to-GPU communications.
Software integration across this layer is handled through DOCA (Data Center Infrastructure-on-a-Chip), which acts as the development framework for DPUs analogously to CUDA for GPUs. DOCA provides application programming interfaces that expose BlueField's hardware security and storage acceleration functions to enterprise software developers and infrastructure providers. By shifting operational evaluation from isolated token-generation metrics to secure task completion, Nvidia is positioning its networking and DPU hardware as an essential control plane for enterprise agent deployments.
Sources
Written by
The Company Wire
Inside the companies building what’s next. Reporting on startups, technology, funding and the people shaping them.