Global Post-Quantum Cryptography Regulations Target 2030 Deadlines Amid Divergent Regional Rules
Multinational enterprises face a patchwork of compliance requirements as governments push toward post-quantum encryption standards.
As governments worldwide prepare for quantum computing threats to modern encryption, regulatory frameworks are clustering around target deadlines in 2030. However, differing regional scopes and compliance requirements are forcing multinational corporations to manage multiple migration strategies simultaneously, as first reported by SiliconANGLE.
The divergence in national regulatory strategies is already evident across key global jurisdictions. Australia has adopted a strict approach by demanding a complete transition to post-quantum cryptography (PQC). In contrast, nations across Scandinavia and the Baltic region are aligning their organizational roadmaps and high-risk infrastructure rules with timelines established by the European Union.
In the United States, federal policy directives are similarly pushing public sector agencies toward the end-of-decade target. Executive Order 14412 mandates that federal agencies assign dedicated PQC migration leaders and complete the transition of key establishment protocols for high-value assets and high-impact systems to PQC by Dec. 31, 2030.
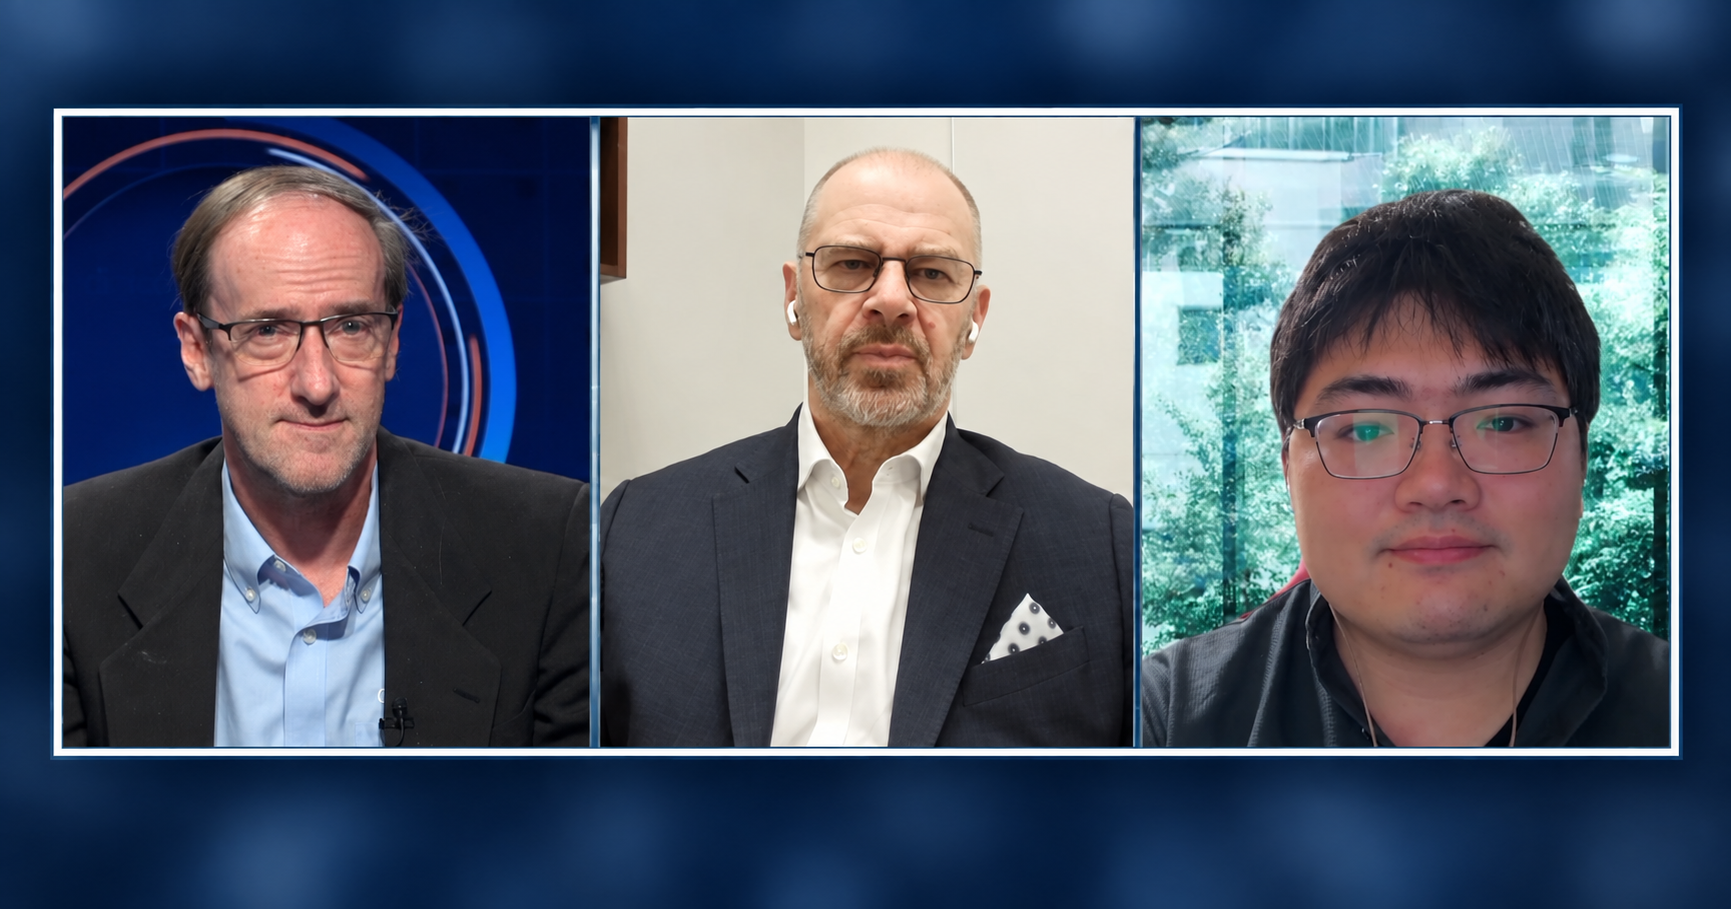
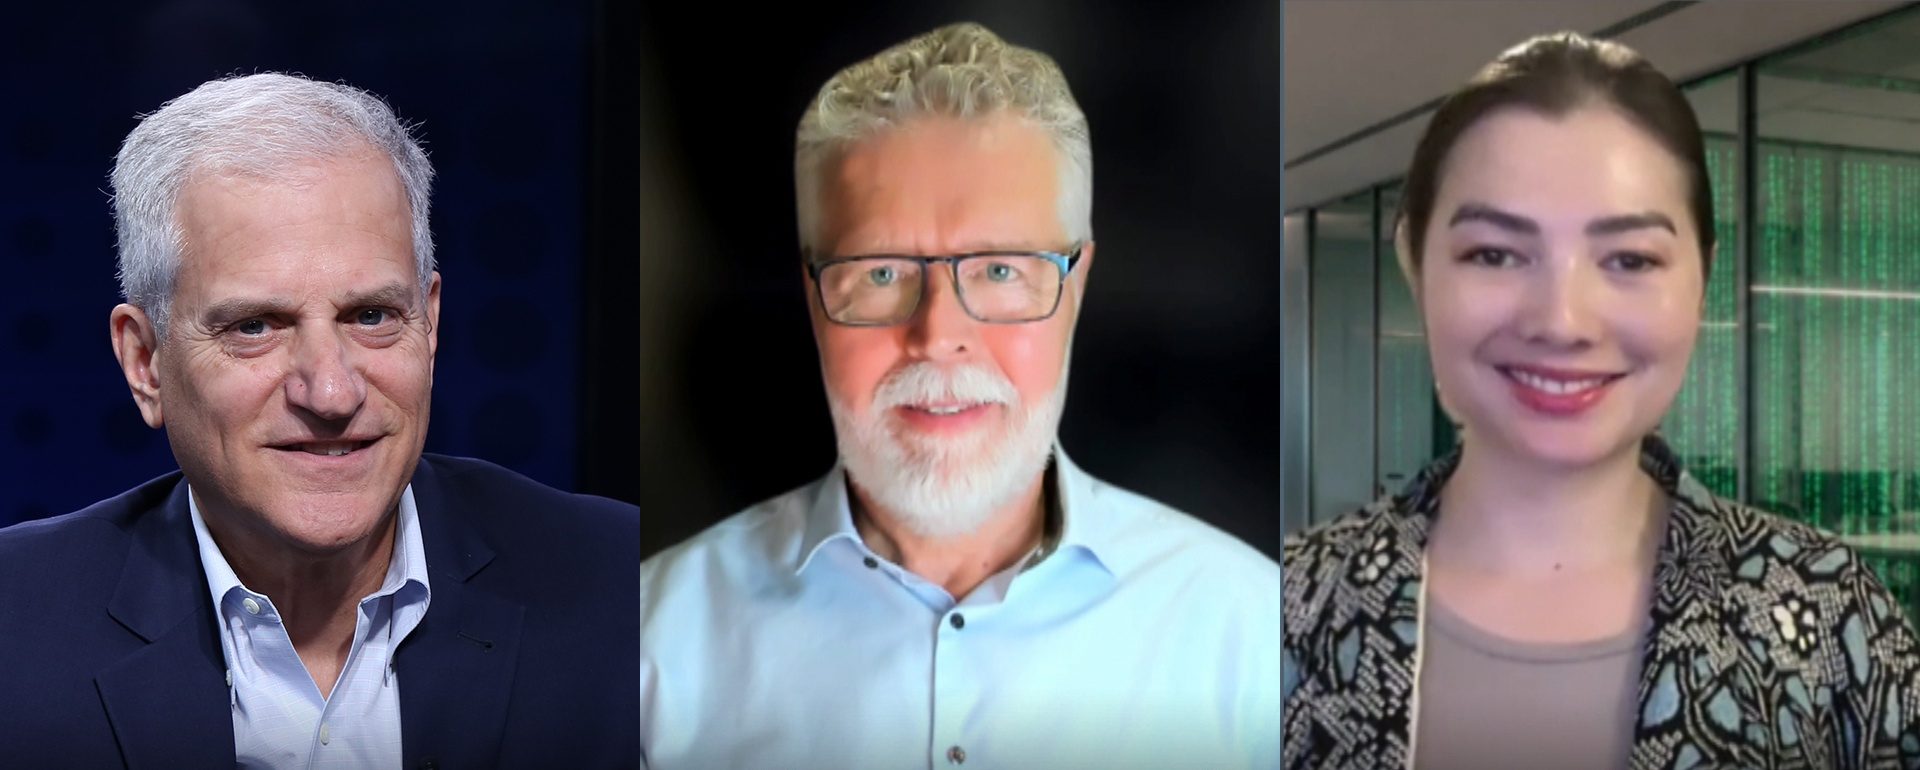
Speaking during DigiCert Inc.’s World Quantum Readiness Day, industry leaders highlighted how these contrasting legislative efforts are impacting enterprise security plans. Naomi Wynn, chief executive officer of National Energy Public Key Infrastructure (NEPKI), noted during an interview on SiliconANGLE’s livestreaming platform theCUBE that Australian authorities are setting rigorous benchmarks for organizations under their jurisdiction, requiring complete PQC compliance and total migration by 2030.
Beyond government-mandated timelines, international variations in post-quantum technical standards present additional administrative friction. Jostein Stokkan, product manager of service offerings at IT infrastructure provider Atea Norge AS, emphasized during the panel moderated by DigiCert senior director Dean Coclin that enterprise IT environments must build adaptive capabilities to navigate shifting cryptographic requirements across markets.
Stokkan explained that enabling organizations to become more crypto agile will simplify the transition, allowing technology teams to adjust to emerging encryption formats and algorithm shifts as regulatory demands evolve across various jurisdictions.
Despite the clear policy targets established by major economies, practical implementation guidelines remain an area of uncertainty for many operators. Wynn stressed that because no universal template exists for PQC migration, enterprise technology leaders must tailor their transition plans while anticipating clearer official guidance on compliance expectations in the coming year.
Sources
Written by
The Company Wire
Inside the companies building what’s next. Reporting on startups, technology, funding and the people shaping them.